
Visitors
Is it fast and usable?
Core Web Vitals on desktop and mobile, accessibility checks, and broken links, images and console errors from a real browser.
Example findingLCP 4.8s on mobile: hero image is 2.1 MB
Website auditWebsite · Security · CodeWebsite audit · Security scan · Code scanner · Fixes for your stack
Scanverra checks any URL for performance, SEO, accessibility and security issues, scans your code for secrets and vulnerable dependencies, and writes the fix for your stack.
npx @scanverra/cli scan .Runs on your machine. Only findings are uploaded, never your source code. Needs a free API key.
No sign-up for website audits · Free plan, no card · 5 free scans a month on each advanced tool
See a sample reportAgentic Browsing
AI accessibility · llms.txt · structured data · robots.txt
Detects your stack and writes fixes for it: 35+ frameworks and platforms
Watch the 1-minute story
Watch one scan find the bugs hiding in a website, rank them, write the fix for your stack and prove it worked.
No sign-up. Results in about a minute.
Your website looks fine. But underneath, it's crawling with bugs. Meet Scanverra, the bug hunter for your website and your code. Paste your URL and the hunt begins. Speed, security, SEO and your stack, checked in about a minute. Every bug gets caught. Leaked keys, slow pages, missing tags. Your report ranks every bug by impact, so you know what to fix first. Each one comes with the fix, written for your stack. Copy it, or open a pull request. Then re-scan to verify, and watch your scores climb. Schedule scans to keep patrolling, with five scanners for your site and your code. Find what's broken before you ship. Start your first hunt free. No sign-up needed.
One scan, four points of view
Most tools look from one angle. Scanverra checks what your visitors, search engines, attackers and your own code each run into.
Visitors
Core Web Vitals on desktop and mobile, accessibility checks, and broken links, images and console errors from a real browser.
Search engines and AI search
Titles, canonicals, structured data, sitemaps and robots.txt, plus how ready your pages are to be quoted in AI answers.
Attackers
Security headers, cookies, TLS, mixed content and secrets leaked in page scripts, ranked by severity.
Your code and AI agents
Secrets, vulnerable dependencies, unsafe code patterns and risky AI-agent configs, scanned in your repo or locally with the CLI.
Performance, security, SEO and code scanning in one workspace, with an AI-written fix attached to every finding.
Performance
Fast on mobile
AI agents now write, run and ship your code. The repo scanner checks for the new ways that goes wrong, alongside the secrets, SAST and dependency checks you already run.
Attackers hide instructions in files your coding agents trust: rules files, CLAUDE.md, copilot-instructions.md. Invisible Unicode, injected prompts and exfiltration commands turn the agent against your own repo, at machine speed.
Agents run shell commands, launch MCP servers and commit code, often with approvals switched off. One auto-approve setting or unpinned MCP package is all a poisoned prompt needs to reach a laptop or a CI runner.
Few teams can list the models, providers and MCP servers their code uses. Every scan builds that inventory and checks it against a policy file you commit, so an unapproved model fails the scan instead of surprising an auditor.
Also runs in the CLI and on every pull request.
Specialized tools
Four tools for when a quick audit is not enough. A free account includes 5 scans a month on each.
0
Critical
1
High
3
Medium
2
Low
AI assessment: Missing Content-Security-Policy header exposes the site to XSS. Cookie flags and HSTS are configured correctly.
Inspect HTTP headers, scan inline scripts for leaked secrets, detect CSRF gaps, mixed content, and missing SRI - with a 0–100 risk score and AI assessment.
1.8s
LCP
0.02
CLS
180ms
TBT
Loads your site in a real browser, checks every link, validates images, checks forms, and captures a full page-load filmstrip.
Fair · Repo Health
Quality Gate: FAILED1
Secrets
4
SAST
2
Dep CVEs
Connect GitHub or Bitbucket and scan any repository for SAST issues, hardcoded secrets, dependency CVEs and IaC misconfigurations, with AI fixes and one-click pull requests on GitHub.
Pass
GEO ready
Pass
E-E-A-T
Live
Search Console
Scan any page for on-page SEO, GEO/AI-search readiness, and E-E-A-T trust signals. Optionally render JavaScript, connect Google Search Console for real ranking data, and get AI-written fixes.
Scheduled scans, score-drop alerts, history, side-by-side comparisons and client-ready reports.
Compare
See every metric change across scans in one matrix
Speed
Track Core Web Vitals
SEO
issues found
Browser Audit
Crawl every link and form
AI Chat
Ask about any finding
Health Score
Free instant website assessment
PDF Reports
Client-ready audit reports
Security
Catch risks before attackers do
Score History
Track every release
For developers
Run the same checks from your terminal, CI pipeline, editor or your own scripts.
Your code stays on your machine
The CLI downloads Scanverra's signed rules, scans locally and uploads only findings: file, line, rule and fix suggestion. File contents and secret values are never uploaded.
The Free plan includes 1 API key. Uploaded CLI scans count toward your monthly free Repo Scanner scans.
npx @scanverra/cli scan .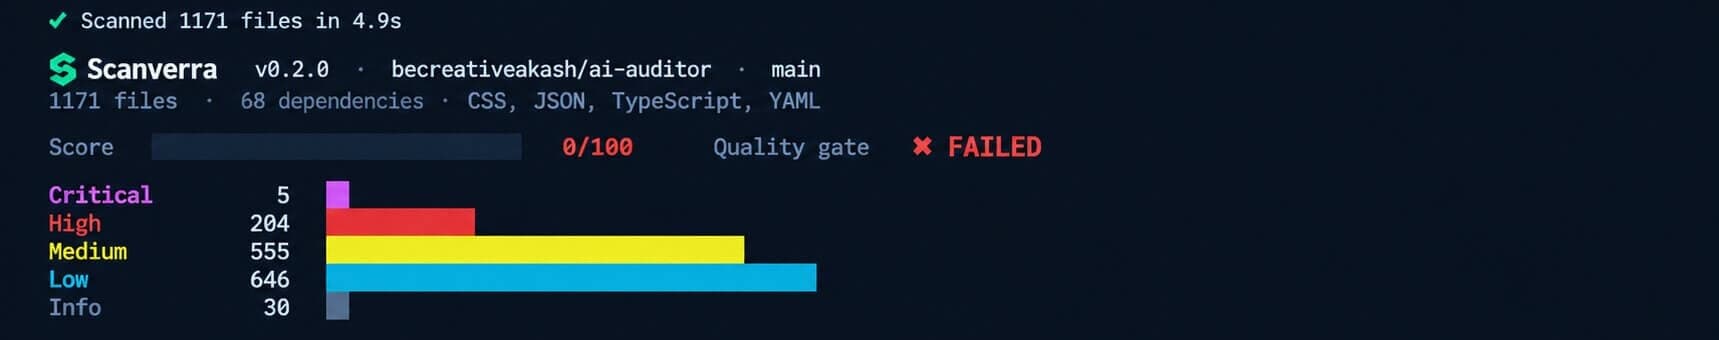
.github/workflows/scanverra.yml
on: [push, pull_request]
jobs:
  scanverra:
    runs-on: ubuntu-latest
    permissions:
      contents: read
      security-events: write
    steps:
      - uses: actions/checkout@v4
      - uses: scanverra/scan-action@v1
        with:
          api-key: ${{ secrets.SCANVERRA_API_KEY }}
          fail-on: high
Pricing
Website audits are free and unlimited. A free account adds monthly scans on every advanced tool.
Free
Forever free - no card required
Pro
Most popularBilled monthly, cancel anytime
A website audit is an automated analysis of a site's performance, SEO, accessibility, and security. It measures how fast the page loads, whether it ranks well in search, whether it meets accessibility standards, and whether it has security vulnerabilities - then explains what to fix.
PageSpeed Insights gives you scores and a list of issues for one page. Scanverra also detects your tech stack and writes the fix for it, checks security headers and leaked secrets, crawls with a real browser, and scans the code behind the site for secrets and vulnerable dependencies.
No. Website audits run without an account. A free account (Google, GitHub or email) saves your reports, adds score history and AI chat on your results, and unlocks the free monthly scans on the other tools. Scheduled scans are part of Pro.
Not with the CLI. It downloads Scanverra's signed rules, scans on your machine and uploads only findings (file path, line, rule and fix suggestion). File contents and secret values stay local unless you pass --include-code. The web Repo Scanner is different: it reads your repository through GitHub or Bitbucket to scan it on our servers.
Only what is needed to explain and fix the findings. For a website audit, that is the scan results for a public page: issues, metrics and the detected stack. For code, it is the findings plus, on the web Repo Scanner, the flagged code snippets (and the file being changed when you open a fix pull request). CLI uploads contain no code unless you pass --include-code.
A website audit usually takes 30 to 90 seconds, because the page is loaded in a real browser at desktop and mobile sizes. Browser audits take about a minute depending on site size. Repo scans depend on repository size, and CLI scans usually finish in seconds.
Scanverra detects 35+ frameworks including Next.js, React, Vue, Angular, Svelte, WordPress, Webflow, Wix, Shopify, WooCommerce, Ghost, Framer, and more - then tailors every fix to your specific stack.
Yes. Website audits are free and unlimited, no account needed, with a 15-minute wait before re-auditing the same site. A free account skips that wait for 5 audits a month. With a free account, each advanced tool includes free scans every month: Browser Audit 5, Security Scanner 5, Repo Scanner 5 (including CLI uploads) and SEO Optimizer 5. Pro removes the limits and adds scheduled scans with alerts.
Free to start, no card required
Run a free website audit now. Add the CLI to your pipeline when you're ready.
No sign-up for website audits · Code scans run locally with the CLI